
Operating System
Cyber threats evolve daily, but strong internal safeguards remain your first line of defense. These 10 proven strategies help cybersecurity leaders build a resilient data protection framework that adapts to modern risks while maintaining operational efficiency.
Role-Based Access Control Implementation
Tired of sifting through compliance reports only to find employees with access they shouldn’t have? Role-Based Access Control (RBAC) solves this by tying permissions directly to job functions—not just individual users.
With RBAC, you can assign HR managers access to payroll systems while marketing teams only see campaign analytics. Platforms like Microsoft Active Directory or Okta automate this with granular controls, reducing insider threats by up to 70%—and streamlining audits for industries like healthcare or finance. The best part? You can revoke access instantly when roles change, like when an employee moves departments.
This is the go-to safeguard for companies handling sensitive data, especially those in regulated sectors where compliance is non-negotiable. ⚡
Automated Data Encryption Policies
Accidental data leaks or malicious intercepts can cripple a business—automated encryption policies act as an invisible shield for your most sensitive files. Unlike manual encryption, these policies enforce AES-256 encryption by default for emails, databases, and cloud transfers, ensuring compliance with standards like HIPAA, GDPR, and SOC 2 without requiring employee intervention.
Modern solutions like Symantec Encryption Desktop or Microsoft Purview Message Encryption integrate seamlessly with existing workflows, encrypting data both at rest (stored files) and in transit (emails, API calls). They also support key escrow for authorized access during audits, while automated certificate rotation prevents vulnerabilities from expired keys. For remote teams, VPN-embedded encryption ensures secure connections even on public Wi-Fi.
This safeguard is a must for industries handling patient records, financial data, or proprietary research. Start with email encryption for high-risk communications, then expand to file-sharing platforms and databases—a phased approach that minimizes disruption while maximizing protection. ✨
Continuous Employee Security Training
Even the strongest firewalls can’t stop a curious employee from clicking a malicious link—60% of breaches start with human error. Continuous employee security training closes this gap by turning staff into your first line of defense through quarterly phishing simulations and gamified cybersecurity modules.
Platforms like KnowBe4 or Proofpoint deliver tailored phishing tests that mimic real-world attacks, while interactive modules teach best practices (e.g., spotting spoofed emails or securing remote connections). These programs adapt to remote workforces with mobile-friendly modules and frequent turnover by onboarding new hires with bite-sized, scenario-based lessons—no dry manuals required.
Ideal for SMBs to enterprises, this approach cuts human-related breaches by up to 70% while keeping teams engaged. 💡
Network Segmentation Architecture
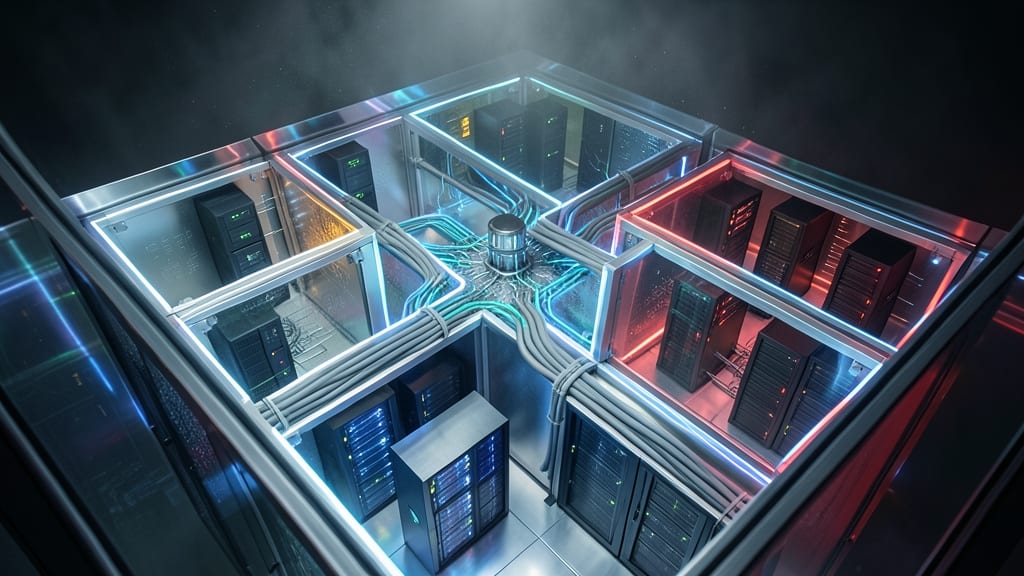
When a breach happens, the last thing you want is for attackers to wander freely through your network like it’s an all-you-can-eat buffet. Network segmentation architecture acts as a series of digital walls, isolating critical systems (like finance or patient records) from general traffic and stopping lateral movement in its tracks.
This approach divides your network into micro-segments—think separate zones for HR, R&D, and guest Wi-Fi—each with its own access controls. Solutions like Palo Alto Networks VM-Series or Cisco ACI automate this with zero-trust principles, ensuring only approved devices communicate across segments. For healthcare, HIPAA compliance becomes effortless when PHI data stays locked in its own zone.
Financial institutions and healthcare providers see the biggest payoff, but even mid-sized businesses benefit from containing ransomware outbreaks to a single department. The result? Contained breaches, faster recovery, and peace of mind. ✨
Endpoint Detection and Response
Your employees’ devices—laptops, smartphones, even that smart coffee maker in the break room—are potential entry points for cyberattacks. Endpoint Detection and Response (EDR) closes this gap by monitoring every connected device in real-time, not just traditional endpoints.
Solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint provide sub-second threat detection across IoT, BYOD, and corporate devices, with automated responses that quarantine malicious activity instantly. Unlike traditional antivirus, EDR uses behavioral analysis to spot zero-day exploits and insider threats before they escalate. The result? Mean time to detection (MTTD) drops from hours to minutes, giving your team critical seconds to act.
This is a game-changer for industries like healthcare or finance, where compliance demands visibility across all devices. Even small businesses benefit—EDR scales to protect remote teams without overwhelming IT staff. 💻
Privileged Access Management
Credential stuffing attacks exploit one weak link: standing administrative privileges that never expire. Privileged Access Management (PAM) flips the script by granting elevated access only when—and for as long as—it’s genuinely needed, then revoking it automatically.
Modern PAM solutions like CyberArk or BeyondTrust implement just-in-time (JIT) access, where admins request temporary elevation with approval workflows, session recording, and auto-revocation after 15–60 minutes. This slashes the attack surface by 80% while maintaining audit trails for compliance. Multi-factor authentication (MFA) further locks down these sessions, ensuring even compromised credentials can’t escalate privileges.
Perfect for finance, healthcare, and government sectors where regulatory scrutiny is intense, PAM turns "always-on" admin accounts into time-limited, monitored sessions. The result? Fewer breaches and easier compliance—without sacrificing productivity. 💪
Data Loss Prevention Monitoring
Accidental data leaks often happen in plain sight—an employee emailing confidential files to the wrong address or plugging a USB drive into an unsecured port. Data Loss Prevention (DLP) monitoring stops these breaches before they escalate by scanning all outgoing communications and storage devices in real time.
Modern DLP solutions like Symantec DLP or Microsoft Purview use AI-driven pattern recognition to flag sensitive data (credit card numbers, PII, trade secrets) across email, cloud storage, and removable media. They can even auto-redact or block transfers entirely, with customizable policies for different data types. For regulated industries, these tools simplify compliance by generating audit trails for HIPAA, GDPR, or CCPA requirements.
This safeguard is non-negotiable for legal firms, healthcare providers, or R&D teams where intellectual property is the crown jewel. Even small businesses handling customer data should prioritize it—because one accidental click can cost millions. 💪
Incident Response Playbooks
When a breach hits, every second counts—yet many organizations waste critical minutes scrambling for a response. Incident Response Playbooks turn chaos into action by providing step-by-step procedures for common threats like ransomware, phishing, or credential leaks, ensuring your team reacts with precision instead of panic.
These playbooks include predefined escalation paths, containment protocols, and clear communication templates tailored to your infrastructure. Tools like Splunk ES or IBM Resilient automate workflows, while frameworks from NIST SP 800-61 ensure compliance-ready documentation. Studies show they cut recovery time by 40%—meaning less downtime and fewer costly mistakes.
Perfect for mid-sized businesses to enterprises, these playbooks are especially critical for sectors like finance or healthcare where regulatory penalties loom. Start with a phishing response playbook to test your team’s readiness before expanding. ✨
Third-Party Risk Assessment
Your supply chain is only as strong as its weakest link—and 60% of breaches actually start with third-party vulnerabilities. A Third-Party Risk Assessment systematically evaluates vendors and partners before they become gateways for attacks, using a combination of automated questionnaires and penetration testing to uncover hidden risks.
Tools like SecurityScorecard or BitSight provide real-time visibility into a vendor’s security posture, scoring them on factors like patch management, encryption standards, and compliance adherence. Automated questionnaires ensure consistent due diligence, while simulated attacks reveal vulnerabilities even the most thorough audits might miss. This proactive approach turns potential weak points into fortified partnerships.
Ideal for organizations relying on outsourced IT, cloud services, or global suppliers, this safeguard is especially critical for financial institutions and healthcare providers where third-party breaches carry severe regulatory penalties. 💪
Behavioral Analytics for Anomaly Detection
While firewalls and antivirus tools block known threats, behavioral analytics fills the gap by analyzing how users interact with systems—spotting subtle red flags like late-night logins or unusual data access patterns that signal compromised accounts.
Solutions like Darktrace or Exabeam use AI-driven anomaly detection to baseline normal behavior, then flag deviations with 95% accuracy for threats like insider leaks or APTs. These tools integrate with SIEM systems and require zero manual rule updates, adapting to evolving attack tactics in real time.
Ideal for organizations handling sensitive IP or financial data, behavioral analytics acts as a force multiplier for SOC teams, cutting investigation time by 60%+ while reducing false positives. 💡