
Operating System
Cyber threats evolve daily, but small proactive changes can transform your business’s security posture. These ten actionable strategies go beyond basic antivirus to create a layered defense against phishing, ransomware, and data breaches—without requiring a massive budget.
Multi-factor authentication for all accounts
Credential stuffing attacks account for 99.9% of successful breaches—but multi-factor authentication (MFA) can stop them dead in their tracks. Unlike passwords alone, MFA adds a second layer of verification, making it nearly impossible for hackers to hijack accounts even if they crack your login details.
Most services now support SMS codes, authenticator apps (like Google Authenticator or Microsoft Authenticator), or hardware keys for frictionless security. For remote teams, YubiKey or Duo Security provide hardware-based MFA that’s immune to SIM-swapping attacks. Even free options like Microsoft’s built-in MFA or Google’s 2-Step Verification offer robust protection without breaking the bank.
Prioritize MFA for email, financial accounts, and cloud services—these are the top targets for attackers. Remote workers and executives should enable it first, as they’re often the most vulnerable. With just a few clicks, you can eliminate 99.9% of credential stuffing risks and sleep easier knowing your accounts are locked down. ⚡
Zero-trust network architecture implementation
Forget firewalls that only guard the perimeter—zero-trust architecture treats every device and user as a potential threat, even inside your network. This modern approach eliminates the "trusted by default" mindset by requiring continuous verification through identity-based access controls and micro-segmentation.
With solutions like Microsoft Azure AD Zero Trust or Cisco SecureX, you enforce least-privilege access, encrypt all traffic, and monitor behavior in real time. The result? 90% fewer lateral movement attacks (where hackers move freely after breaching one system) and compliance with frameworks like NIST SP 800-207 for regulated industries.
Perfect for healthcare providers handling PHI, financial firms processing payments, or any business storing customer data—this isn’t just theory. Start with piloting conditional access policies in your cloud apps to see immediate impact. ✨
Automated patch management system
Malware exploits zero-day vulnerabilities within hours of discovery—but an automated patch management system closes those gaps before attackers can strike. Unlike manual updates that get delayed or ignored, these systems prioritize critical OS and application patches (like the Log4j or PrintNightmare exploits) with 24-hour turnaround, ensuring your systems stay hardened against the latest threats.
Tools like Microsoft Endpoint Configuration Manager or SolarWinds Patch Manager scan your environment, classify vulnerabilities by risk level, and deploy fixes automatically—even for hundreds of devices—while minimizing downtime. They also maintain audit logs for compliance with PCI DSS, HIPAA, or GDPR, proving you’re proactive about security without the manual overhead.
This is the silent guardian for businesses where downtime costs thousands per hour—think healthcare providers, financial institutions, or any organization running legacy systems. With 90% of breaches linked to unpatched software, this is one upgrade that pays for itself in risk reduction alone. 💪
Phishing simulation training programs
Your employees are your strongest—and weakest—link in cybersecurity. Phishing simulation programs like KnowBe4 or GoPhish turn your team into proactive defenders by mimicking real-world attacks, from fake invoices to CEO impersonations, and tracking how quickly they spot red flags.
These platforms offer role-specific scenarios (e.g., executives get CEO fraud tests, IT staff face technical exploit simulations) and real-time reporting to measure improvement over time. For example, KnowBe4’s phishing test library includes over 2,000 templates, while GoPhish provides open-source flexibility for custom campaigns. Most systems integrate with Microsoft 365 or Slack to deliver simulations seamlessly.
Perfect for businesses where human error drives breaches—like healthcare or finance—these tools reduce click rates by 70% within months. Start with a pilot program to train your most vulnerable teams first. ✨
Endpoint Detection and response tools
Traditional antivirus can’t stop modern ransomware—it needs Endpoint Detection and Response (EDR) tools that hunt threats in real time. These solutions go beyond signature-based scanning to detect suspicious behavior, like unauthorized data exfiltration or lateral movement, before encryption locks your files.
Platforms like CrowdStrike Falcon or Microsoft Defender for Endpoint offer AI-driven behavioral analysis, automated containment of threats, and detailed forensic reports. They integrate with your existing security stack and work across Windows, macOS, and Linux—critical for BYOD environments where personal devices connect to corporate networks. 🔧
Encrypted cloud storage and backups
Ransomware attacks cripple businesses daily—yet immutable backups and AES-256 encryption can neutralize them before they cause damage. Unlike traditional cloud storage, solutions like Backblaze B2 or Wasabi Hot Storage combine military-grade encryption with versioned backups that can’t be altered or deleted, even by admins.
You get zero-configuration setup (files auto-backup in the background) and unlimited storage for a flat monthly fee. The immutable retention policy ensures ransomware can’t encrypt your backups—critical for healthcare (HIPAA) or legal (attorney-client privilege) compliance. Recovery takes minutes, not days.
Perfect for SMBs handling sensitive data or solo professionals who can’t afford downtime. 💻
Network segmentation for critical systems
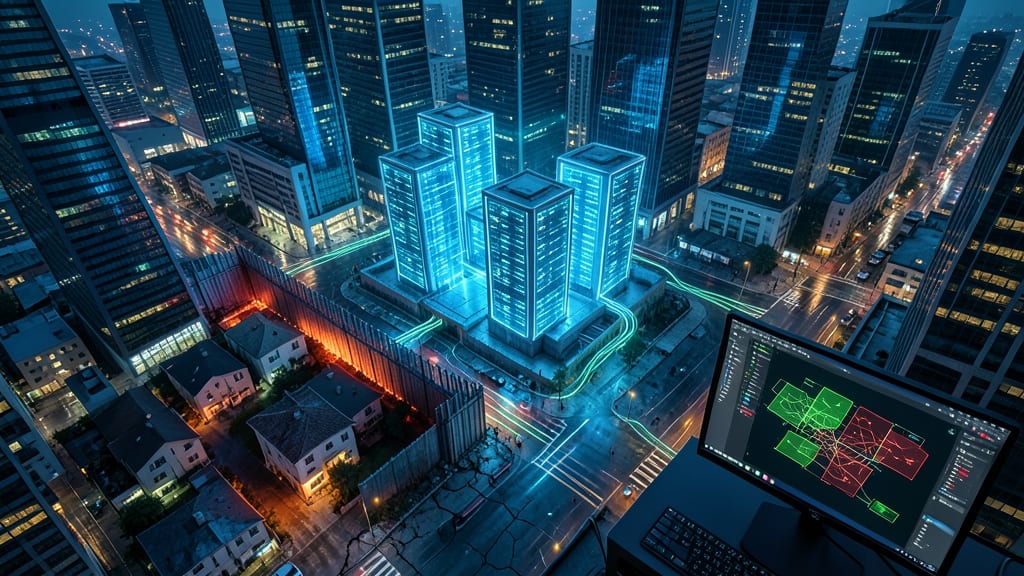
Think of your network like a city: if attackers breach one district, they shouldn’t be able to wander freely through the financial core. Network segmentation creates virtual walls around your most sensitive systems—like HR databases, payment gateways, or R&D servers—so even if one area is compromised, the rest stay locked down.
Most SMBs can implement this with existing hardware using built-in VLANs (Virtual LANs) on routers like the Ubiquiti UniFi or Cisco Meraki, which cost under $500. For cloud environments, tools like AWS VPC or Azure Network Security Groups offer granular control without complex setups. The key is isolating traffic by function—no guest Wi-Fi should route to your accounting server, and dev machines shouldn’t access production databases.
This is the #1 defense against lateral movement, where attackers hop between systems after breaching one. For businesses handling customer data or PCI compliance, segmentation often satisfies audit requirements with minimal overhead. Start with your most critical assets—you’ll sleep better knowing they’re walled off from the rest. ✨
AI-powered threat intelligence feeds
Cybercriminals aren’t waiting for vulnerabilities—so why should you? AI-powered threat intelligence feeds analyze global attack patterns in real-time, flagging zero-day exploits and emerging malware before they hit your systems. Unlike traditional signature-based defenses, these tools use machine learning models trained on billions of threat samples to predict attack vectors with up to 90% accuracy.
Solutions like Darktrace or CrowdStrike’s Threat Graph integrate with your SIEM (Security Information and Event Management) to automatically adjust firewall rules and block suspicious IPs. They’re especially valuable for businesses processing high-value transactions, where attackers target payment gateways or customer databases with surgical precision. The best feeds also provide customizable alert thresholds, so you avoid false positives while catching genuine threats.
This is the ultimate defense for sectors where fraud patterns evolve faster than traditional security tools can keep up. If your business handles sensitive data or operates in fintech, e-commerce, or healthcare, AI threat intelligence isn’t just a nice-to-have—it’s your early warning system. ✨
Vendor risk assessment and contracts
Before integrating a new cloud provider, SaaS tool, or contractor, you’re essentially inviting them into your digital ecosystem—without checking their security credentials. Vendor Risk Assessments (VRAs) close this gap by evaluating third-party security controls before contracts are signed, ensuring they align with your NIST or ISO 27001 baseline.
Start by auditing vendors using frameworks like SOC 2 Type II or ISO 27001 certifications, then probe deeper with penetration testing requirements and incident response SLAs. Tools like SecurityScorecard or BitSight automate this process, scoring vendors on real-time risk factors. For contractors, include right-to-audit clauses in contracts to verify compliance during engagements.
This is your first line of defense against supply-chain attacks—where breaches like SolarWinds or Kaseya began. Healthcare providers, fintech startups, and government contractors should prioritize VRAs, but even small businesses using third-party payment processors benefit from this due diligence. 💪
Cybersecurity incident response plan
When a breach happens, every minute counts—yet most businesses scramble without a plan. A cybersecurity incident response plan turns chaos into action by defining pre-assigned roles, step-by-step containment protocols, and escalation paths, cutting downtime by 40% during real incidents.
This isn’t just a document—it includes tabletop exercises to simulate attacks annually, ensuring your team stays sharp. Key components cover communication protocols (who alerts whom), containment steps (isolating affected systems), and forensic preservation (securing evidence for investigations). Frameworks like NIST SP 800-61 provide templates to get started.
Perfect for businesses handling sensitive data or regulated industries (healthcare, finance), but even small teams benefit from the clarity. The real win? Confidence—knowing you’re prepared when it matters most. ✨